Cohort 1 intern
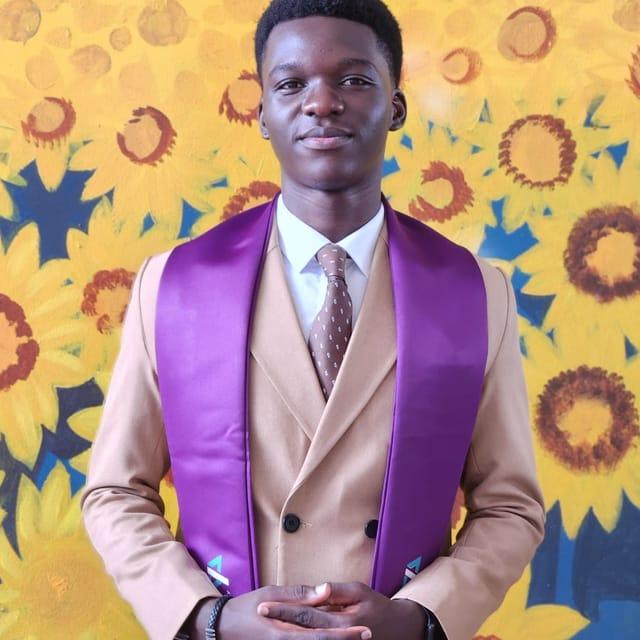
Rwotolara Innocent
In their words.
Before this programme, I had the curiosity and the drive, but I had no evidence that I could actually do the work. Today, I have both. I carried a real breach investigation from a single dismissed alert to a board-ready close. I reconstructed kill chains from raw forensic artefacts. I wrote the risk register, the breach notification to the regulator, the board memo, and the remediation roadmap. I learned that good incident response is not just about finding the threat - it is about documenting it clearly enough that a regulator and a board can act on it. I was humbled, tested, and pushed to become more than just a technical analyst. I am leaving with skills I can prove, confidence I earned the hard way, and a credential that actually means something. If you are willing to do the work, this programme will prepare you for the real world. No shortcuts. Just real growth.